Everything you need to know about apple patches eavesdropping vulnerability in beats.
[ad_1]Security firm Sentinel One has a deeper dive into CVE-2025-20701 here.
Heinze and Steinmetz said last year that the full chain of attacks gave attackers the ability to do other malicious things, including retrieving call history and contacts, and even calling arbitrary numbers. Many of those capabilities are dependent on the specific devices being paired, since the functionality built into them differs from platform to platform.
Devices affected by the Airoha vulnerabilities are by no means alone. In January, researchers disclosed WhisperPair, a series of vulnerabilities that allows an attacker to hijack Bluetooth devices connected through Google Fast Pair, a proprietary protocol belonging to the company. Besides eavesdropping, attackers can exploit the WhisperPair flaws to geolocate devices. The vulnerabilities affect more than a dozen devices from 10 manufacturers, including Sony, Nothing, JBL, OnePlus, and Google itself.
There are few, if any, reports of Bluetooth vulnerabilities like these being actively exploited in the wild. The complexity of such attacks is often high, and an attacker has to continually stay within Bluetooth range of a target while utilizing the exploit. People who think they may be targeted by such attacks should turn off Bluetooth in devices whenever they’re not needed, and remain aware of the risks when Bluetooth is enabled.
[ad_2]
Source link
More on apple patches eavesdropping vulnerability in beats
Stay tuned for updates on apple patches eavesdropping vulnerability in beats as the story develops. Related: Mobile & Accessories.
Frequently Asked Questions
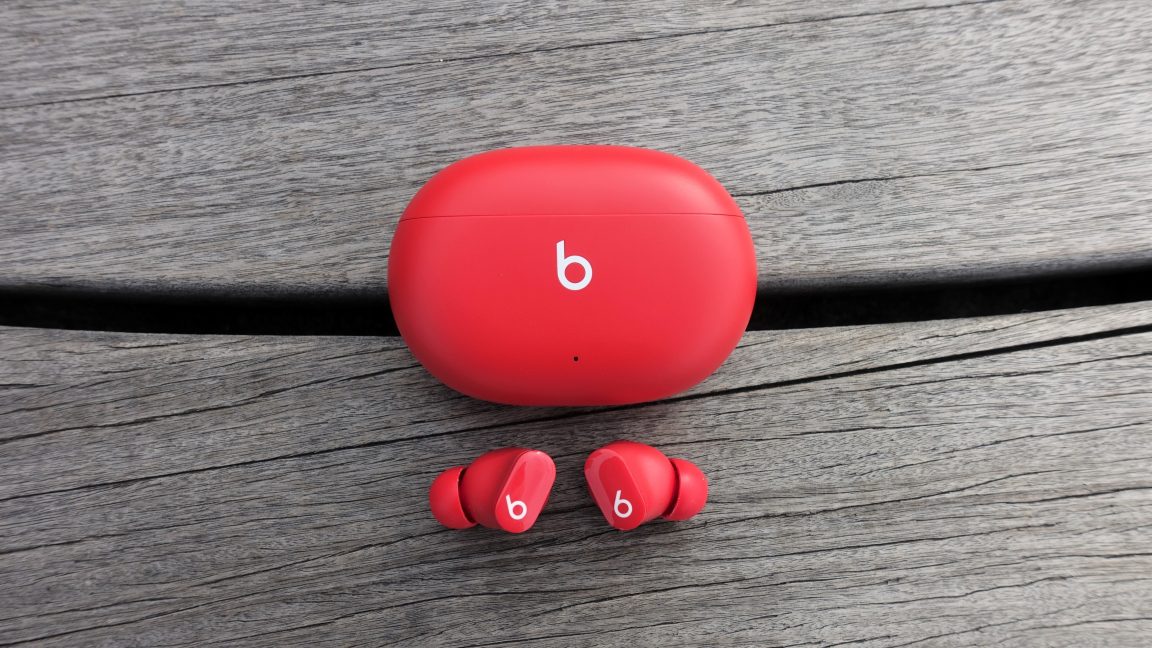
It is an eavesdropping vulnerability affecting Beats Studio Buds that Apple has now patched. Security firm SentinelOne published a deeper dive into the flaw, which involved Airoha chip vulnerabilities.
Researchers Heinze and Steinmetz said the full attack chain could retrieve call history and contacts and even call arbitrary numbers, depending on the paired devices. Besides eavesdropping, the related WhisperPair flaws let attackers geolocate devices.
WhisperPair is a series of vulnerabilities disclosed in January that lets attackers hijack Bluetooth devices connected through Google Fast Pair. It affects more than a dozen devices from 10 manufacturers, including Sony, Nothing, JBL, OnePlus, and Google itself.
The article advises turning off Bluetooth whenever it is not needed and staying aware of the risks when it is enabled. It notes such attacks are rarely exploited in the wild since attackers must stay within Bluetooth range.